---
title: Cribl
description: The Cribl integration routes data from Cribl Stream into Elastic data streams by mapping Cribl source identifiers to Fleet datasets. This lets you keep...
url: https://www.elastic.co/docs/reference/integrations/cribl
products:
- Elastic integrations
applies_to:
- Serverless Observability projects: Generally available
- Serverless Security projects: Generally available
- Elastic Stack: Generally available since 9.4
---
# Cribl
| | |
|-------------------------------------------------------------------------------------------------|--------------------------------|
| **Version** | 1.2.0 ([View all](#changelog)) |
| **Subscription level**[What's this?](https://www.elastic.co/subscriptions) | Basic |
| **Developed by**[What's this?](https://www.elastic.co/docs/reference/integrations/developed-by) | Elastic |
| **Minimum Kibana version(s)** | 9.4.0 |
## Overview
The Cribl integration routes data from Cribl Stream into Elastic data streams by mapping Cribl source identifiers to Fleet datasets. This lets you keep Cribl as your data pipeline layer while using , dashboards, and detections for analytics and operations.
### Compatibility
This integration supports:
- Elastic Stack and Serverless projects with integration package support.
- Cribl Stream deployments that can use the **Elastic Cloud** or **Elasticsearch** destination.
- `logs` and `metrics` data stream types, with dynamic dataset and namespace routing.
### How it works
In Cribl Stream, you set a `_dataId` value on each event. In Fleet, you configure route mappings that map `_dataId` values to target datasets and optional namespaces. Cribl then sends events directly to Elastic using one of its Elastic destinations. The Cribl integration package provides routing configuration and data stream handling, while destination integrations provide parsing pipelines, dashboards, and assets.
## What data does this integration collect?
The Cribl integration collects and routes:
- `logs`: Log events forwarded from Cribl to Elastic data streams.
- `metrics`: Metric events forwarded from Cribl to Elastic data streams.
Use this integration when you want centralized routing and processing in Cribl, while keeping Elastic integration assets for downstream analysis.
## What do I need to use this integration?
To use this integration, you need:
- An Elastic deployment and access to Fleet in Kibana.
- Cribl Stream with permission to configure sources and destinations.
- An Elastic API key for the Cribl destination.
- Index privileges that include at least `auto_configure` and `write` for target `logs-*` and `metrics-*` patterns.
## How do I deploy this integration?
For step-by-step instructions about installing integrations, refer to [Getting started](https://www.elastic.co/guide/en/starting-with-the-elasticsearch-platform-and-its-solutions/current/getting-started-observability.html).
### Onboard and configure
1. Install destination integration assets in Fleet.
- In Kibana, go to the **Integrations** page.
- Install the integration assets for the datasets you plan to route (for example, Cisco ASA).
2. Configure `_dataId` in Cribl sources.
- In Cribl Stream, add a `_dataId` field that identifies the target dataset mapping.
- For more information, see [Cribl data onboarding](https://docs.cribl.io/stream/data-onboarding/).
3. Configure route mappings in the Cribl integration policy in Fleet.
- Map each `_dataId` value to a target data stream dataset.
- Optionally set a namespace. If omitted, `default` is used.
- The Cribl integration does not require Elastic Agent, but Fleet policy configuration is still required.
4. Configure the Elastic destination in Cribl.
- Use either [Elastic Cloud destination](https://docs.cribl.io/stream/destinations-elastic-cloud/) or [Elasticsearch destination](https://docs.cribl.io/stream/destinations-elastic/).
- Set **Cloud ID** (Elastic Cloud) or **Bulk API URLs** (self-managed Elasticsearch).
- Set **Index or Data Stream** based on event type:
- `logs-cribl-default` for logs
- `metrics-cribl-default` for metrics
- Set **API key** to a Base64-encoded Elastic API key value.
### Validation
After deployment:
1. Send test events from Cribl.
2. In Kibana, open **Discover** and confirm documents in the expected `logs-*` or `metrics-*` data streams.
3. Verify dataset and namespace values match the `_dataId` route mappings.
## Troubleshooting
- No data in Elastic:
- Verify destination connectivity (**Cloud ID** or **Bulk API URLs**).
- Confirm API key privileges include `auto_configure` and `write`.
- Data lands in unexpected data streams:
- Check `_dataId` values in Cribl events.
- Check route mappings in the Cribl integration policy.
- Destination integration dashboards are empty:
- Confirm corresponding destination integration assets are installed in Fleet.
- Confirm routed dataset names match what those integration assets expect.
## Performance and scaling
- Use Cribl worker groups and horizontal scaling to handle higher event throughput.
- Tune batching, queueing, and backpressure settings in Cribl before increasing destination concurrency.
- Separate high-volume logs and metrics routes so you can scale and troubleshoot independently.
- Monitor ingestion rate and bulk response errors in both Cribl and Elastic to identify bottlenecks early.
## Reference
### Logs
| Field | Description | Type |
|-----------------------|------------------------|------------------|
| @timestamp | Event timestamp. | date |
| data_stream.dataset | Data stream dataset. | constant_keyword |
| data_stream.namespace | Data stream namespace. | constant_keyword |
| data_stream.type | Data stream type. | constant_keyword |
| event.dataset | Event dataset | constant_keyword |
| event.module | Event module | constant_keyword |
### Metrics
| Field | Description | Type |
|-----------------------|------------------------|------------------|
| @timestamp | Event timestamp. | date |
| data_stream.dataset | Data stream dataset. | constant_keyword |
| data_stream.namespace | Data stream namespace. | constant_keyword |
| data_stream.type | Data stream type. | constant_keyword |
## Screenshots
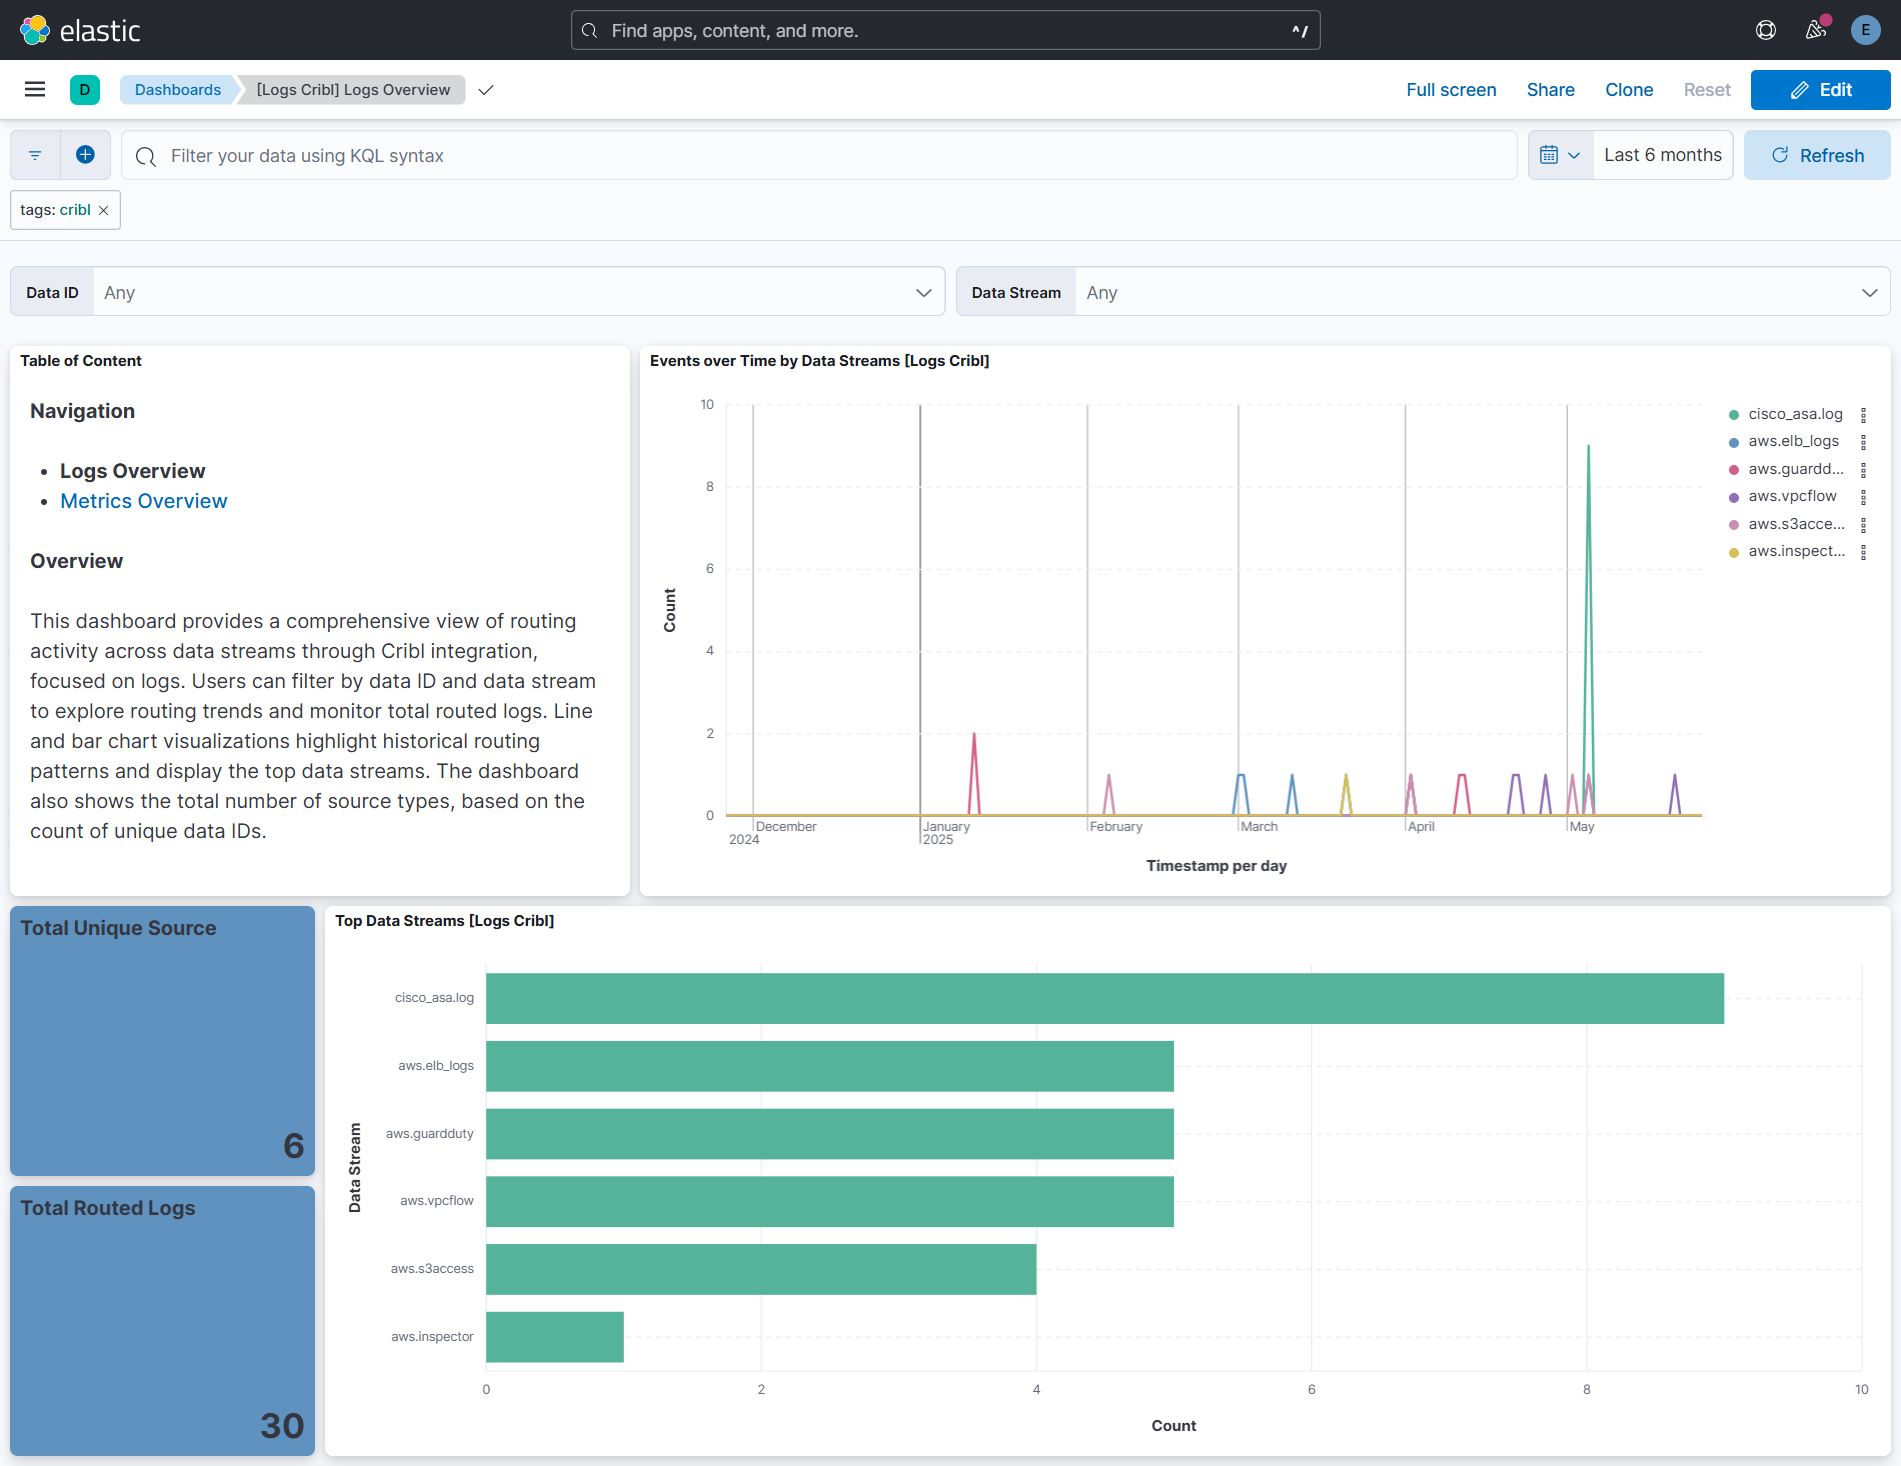
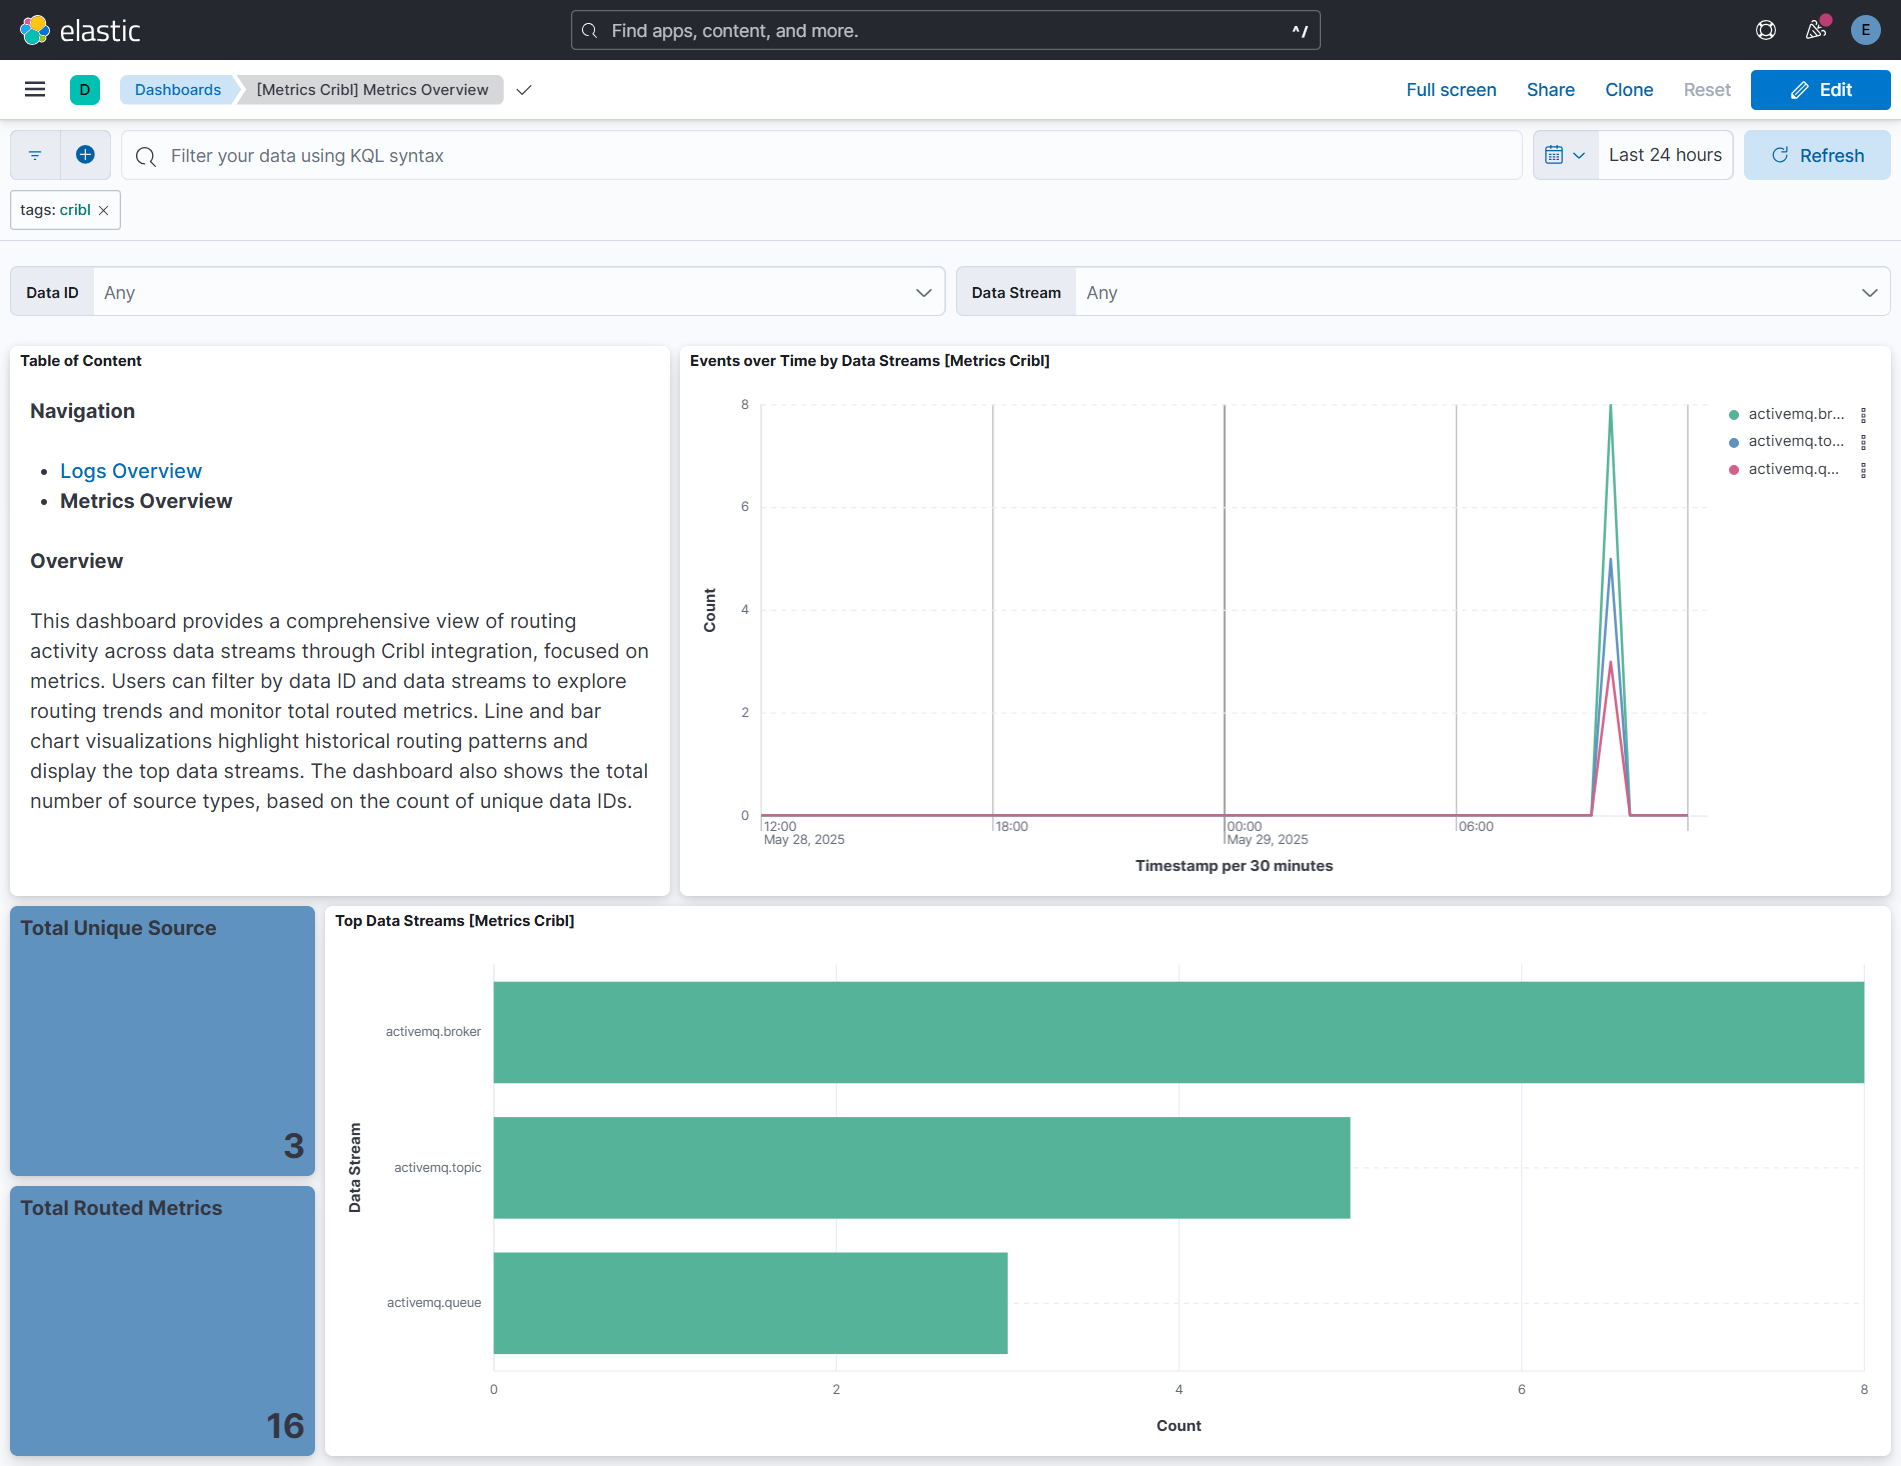
This integration includes one or more Kibana dashboards that visualizes the data collected by the integration. The screenshots below illustrate how the ingested data is displayed.
## Changelog
| Version | Details | Minimum Kibana version |
|-----------|------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|------------------------|
| **1.2.0** | **Enhancement** ([View pull request](https://github.com/elastic/integrations/pull/22088))Changed owners. | 9.4.0 |
| **1.1.1** | **Enhancement** ([View pull request](https://github.com/elastic/integrations/pull/18069))Update documentation to reflect the documentation guidelines. | 9.4.0 |
| **1.1.0** | **Enhancement** ([View pull request](https://github.com/elastic/integrations/pull/17792))Updating documentation to reflect user ability to specify a namespace. | 9.4.0 |
| **1.0.1** | **Bug fix** ([View pull request](https://github.com/elastic/integrations/pull/16443))Rename `_raw` field to `message` only if the `message` field is null. | 9.0.08.13.0 |
| **1.0.0** | **Enhancement** ([View pull request](https://github.com/elastic/integrations/pull/14013))Release package as GA.**Enhancement** ([View pull request](https://github.com/elastic/integrations/pull/14013))Add overview dashboards for logs and metrics.**Enhancement** ([View pull request](https://github.com/elastic/integrations/pull/14013))ECS version updated to 8.17.0. | 9.0.08.13.0 |
| **0.5.1** | **Bug fix** ([View pull request](https://github.com/elastic/integrations/pull/13930))Fix handling of metric event type. | 9.0.08.13.0 |
| **0.5.0** | **Enhancement** ([View pull request](https://github.com/elastic/integrations/pull/12919))Update Kibana constraint to support 9.0.0. | 9.0.08.13.0 |
| **0.4.2** | **Bug fix** ([View pull request](https://github.com/elastic/integrations/pull/11284))Use triple-brace Mustache templating when referencing variables in ingest pipelines. | 8.13.0 |
| **0.4.1** | **Bug fix** ([View pull request](https://github.com/elastic/integrations/pull/10312))Update documentation | 8.13.0 |
| **0.4.0** | **Enhancement** ([View pull request](https://github.com/elastic/integrations/pull/10135))ECS version updated to 8.11.0. Removed import_mappings. Modified the field definitions to remove ECS fields made redundant by the ecs@mappings component template. | 8.13.0 |
| **0.3.0** | **Enhancement** ([View pull request](https://github.com/elastic/integrations/pull/9399))Update manifest format version to v3.0.3. | 8.13.0 |
| **0.2.0** | **Enhancement** ([View pull request](https://github.com/elastic/integrations/pull/9097))Adds the second phase of the Cribl package | 8.13.0 |
| **0.1.2** | **Enhancement** ([View pull request](https://github.com/elastic/integrations/pull/8943))Changed owners | 8.8.0 |
| **0.1.1** | **Enhancement** ([View pull request](https://github.com/elastic/integrations/pull/8487))Update documentation | 8.8.0 |
| **0.1.0** | **Enhancement** ([View pull request](https://github.com/elastic/integrations/pull/8487))Adds the first phase of the Cribl package | 8.8.0 |